With billions of devices connected worldwide, IoT compliance is now a top priority for regulators and manufacturers alike. From privacy breaches to firmware exploits, the consequences of ignoring compliance can be devastating.
This guide breaks down the essential standards, frameworks, and best practices for ensuring your IoT devices meet global compliance expectations in 2025.
TL; DR: Quick Takeaways
- Compliance ensures safety, reliability, and market eligibility.
- Standards such as NIST and ISO/IEC 27400:2022, as well as the EU Cyber Resilience Act, are shaping IoT policy.
- Common failures include poor authentication and inadequate firmware validation.
- Continuous monitoring and documentation are non-negotiable for long-term compliance.
- Compliance improves brand trust, not just risk management.
Why IoT Device Compliance Matters
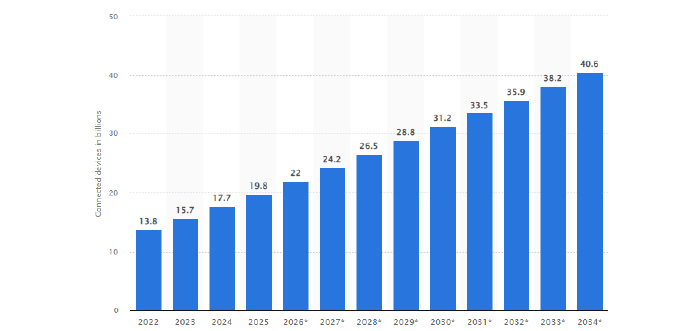
By 2030, over 29 billion IoT devices are expected to be active worldwide (Statista). As adoption grows, regulators are enforcing stricter security standards to prevent data breaches and supply chain risks.
IoT compliance means following legal, technical, and ethical standards to ensure devices are safe and resilient. This covers everything from encryption to lifecycle management.
To understand how artificial intelligence is influencing data protection in connected systems, see How to Use AI to Enhance Data Privacy: Tools and Techniques.
Global Standards Shaping IoT Compliance
Here are the most recognized global standards and regulations guiding IoT device compliance today:
- NIST Cybersecurity for IoT Program (US): Defines best practices for device identity, patch management, and secure development (NIST.gov).
- EU Cyber Resilience Act: Enforces “security by design” principles across all connected devices.
- ISO/IEC 27400:2022: Provides international guidance for IoT risk management and governance (ISO.org).
- California IoT Security Law: The first state law mandating unique device identifiers and reasonable security features (CPO Magazine).
Core Elements of IoT Device Compliance
1. Secure Device Identity
Every device must have a unique identity to prevent spoofing. Certificate-based authentication and hardware-rooted trust (like TPM chips) are now standard in compliant ecosystems.
2. Firmware Integrity and Updates
Outdated firmware is a major risk. Devices must support signed, encrypted, and traceable over-the-air (OTA) updates.
3. Data Privacy and Protection
Regulations like GDPR and the Cyber Resilience Act require encryption in transit and at rest. Manufacturers must also provide users with control over their own data.
4. Supply Chain Transparency
Every component should be verifiable. Maintaining a Software Bill of Materials (SBOM) helps identify vulnerabilities introduced by third-party code.
5. Ongoing Monitoring and Reporting
Compliance doesn’t end at launch. Organizations must monitor device behavior and report incidents within regulated timeframes.
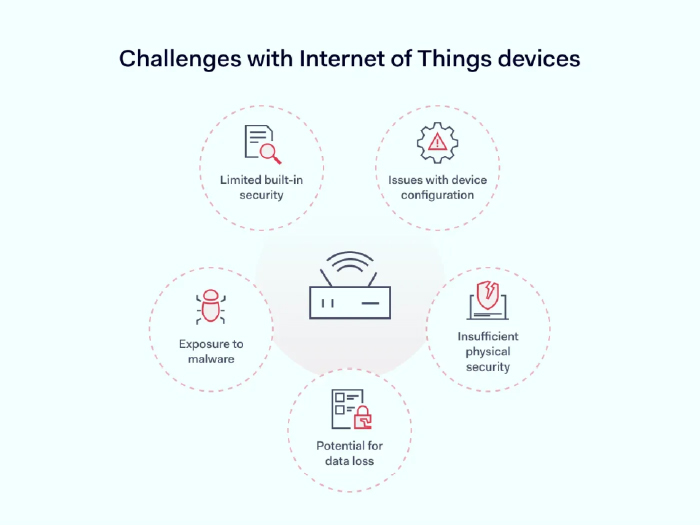
For example, Cisco’s IoT Security report highlights that visibility gaps in device inventories remain a major compliance risk (Cisco).
Source: Nord Layer
Regional Highlights: USA, EU, UK, UAE, and Pakistan
- USA: The NIST IoT Framework guides security architecture and vulnerability reporting.
- EU: CRA mandates continuous patching, vulnerability disclosure, and CE compliance for connected products.
- UK: The PSTI Act (Product Security and Telecommunications Infrastructure) now requires manufacturers to publish support lifecycles.
- UAE: The National Cybersecurity Strategy (2019) sets IoT safety and localization requirements.
- Pakistan: Under its National Cybersecurity Policy, the government encourages IoT risk assessments aligned with ISO standards.
For more on digital transformation and infrastructure compliance, check out Using AI to Automate and Improve Your PPC Campaigns.
How to Build an IoT Compliance Roadmap
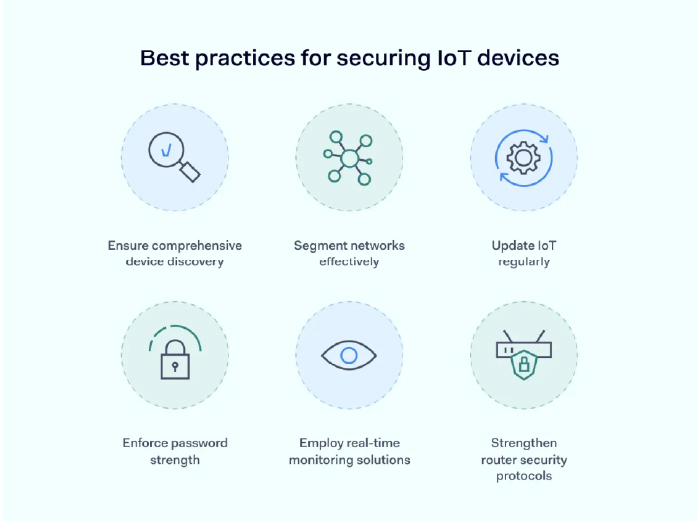
- Identify applicable frameworks: Map out which regulations apply by geography and product type.
- Perform a compliance gap analysis: Compare your product lifecycle against NIST or ISO requirements.
- Implement secure-by-design principles: Integrate encryption, patching, and authentication early in development.
- Maintain documentation: Keep audit logs, firmware signing records, and SBOMs.
- Test regularly: Use penetration testing and automated audits to ensure ongoing compliance.
- Create an incident response plan: Regulators require transparent disclosure of security incidents.
Source: Nord Layer
The Cost of Ignoring IoT Compliance
Non-compliance can lead to product recalls, fines, and brand damage. Under the EU Cyber Resilience Act, companies could face penalties of up to €15 million or 2.5% of annual turnover (European Commission).
Worse, trust loss can be irreversible. Once users doubt the safety of a connected product, retention drops sharply.
Future of IoT Compliance: AI and Automation
By 2026, most large IoT networks will use AI-powered compliance engines to monitor device health and automatically flag anomalies.
Automated policy enforcement tools will map device behavior against frameworks like ISO/IEC 27400 and NIST 8259 to ensure ongoing conformity.
Compliance Builds Confidence
IoT compliance is no longer optional; it’s foundational. By combining robust security, privacy protection, and transparent governance, businesses can confidently scale their connected products worldwide.
Compliance isn’t just regulation, it’s reputation.