As IoT adoption accelerates across homes, industries, and cities, the security risks surrounding connected devices are growing just as fast. Billions of sensors, wearables, smart appliances, medical devices, and industrial control systems are now online, creating an enormous attack surface that cybercriminals are eager to exploit.
A single weak IoT device can compromise an entire network. That is why building a strong IoT security strategy is no longer optional. It is a fundamental requirement for any organisation deploying connected devices in 2025.
This guide breaks down the essential considerations, frameworks, and best practices needed to build a secure, scalable, and future-ready IoT environment.
TL; DR: Quick Takeaways
- IoT security must cover the entire lifecycle from manufacturing to decommissioning
- Identity, authentication, encryption, and firmware security are core foundations
- Supply chain and vendor risks are now top concerns for global regulators
- AI monitoring enables early detection of abnormal device behavior
- Compliance with NIST, ISO, EU CRA, and national regulations is mandatory for market access
Why IoT Security Demands a New Approach
Traditional cybersecurity protects networks, servers, and endpoints. But IoT devices behave differently. They often run outdated firmware, operate with minimal computing power, communicate autonomously, and may sit in remote or unsecured environments.
This means the old perimeter-based model no longer works. Security must be embedded into each device and supported by strong governance.
To understand how IoT fits into the broader connected world, see Integrating Different Smart Home Systems: Tips and Best Practices
1. Start with a Comprehensive Risk Assessment
Every IoT deployment is unique. Before implementing controls, organizations must evaluate potential risks.
Questions to guide your assessment:
- What data will the device collect, store, and transmit
- Does it interact with third-party platforms or cloud services
- What happens if the device fails or is compromised
- Is the device deployed in a secure or public environment
- What regulations govern the industry
Risk assessment ensures that security decisions are based on impact, not assumptions.
2. Strengthen Device Identity and Authentication
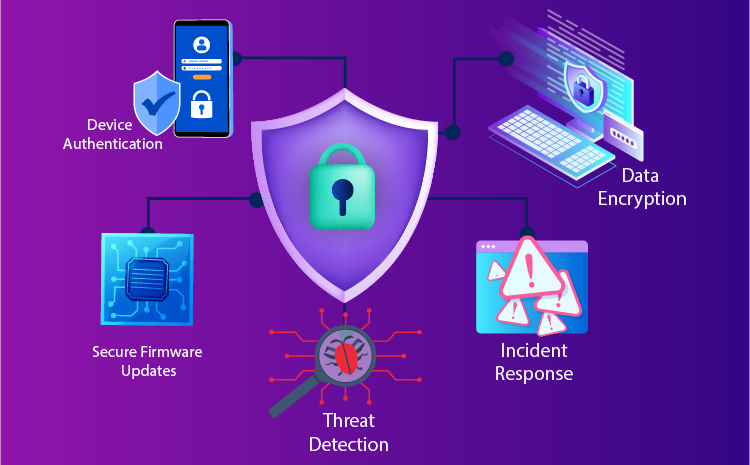
Device identity is the foundation of IoT security. Without it, attackers can clone devices, impersonate legitimate ones, or inject malicious traffic.
Best practices include:
- Hardware-based identity through secure elements
- Unique cryptographic keys for every unit
- Certificate-based authentication
- Mutual authentication between devices, servers, and cloud
Poor device identity is one of the top causes of IoT breaches.
For a deeper look at the privacy challenges behind device identity, read How to Use AI to Enhance Data Privacy: Tools and Techniques on Tech News Tips.
3. Protect Data Through End-to-End Encryption
IoT devices handle sensitive information, often continuously. Encryption prevents attackers from reading or modifying data even if they intercept traffic.
Recommended standards:
- TLS 1.3 for encrypted communication
- AES 256 for data stored on device
- Secure key storage using hardware cryptography
Encryption is essential but only works when paired with secure key management. Keys should never be stored in firmware or accessible memory.
4. Ensure Secure Firmware and OTA Updates
Firmware is the brain of an IoT device. If attackers compromise it, they gain complete control.
Key firmware security measures:
- Signed updates that verify authenticity
- Encrypted over-the-air (OTA) updates
- Secure boot that checks firmware integrity
- Automatic rollback when updates fail
Regulations like the EU Cyber Resilience Act now require manufacturers to provide long-term patching support.
5. Enforce Strong Access Control Policies
Access must be restricted not just for users, but for devices and applications as well.
Recommended access control practices:
- Least privilege for all accounts
- Role-based access for administrators
- Network segmentation separating IoT from critical systems
- Multi-factor authentication for dashboards and control panels
Segmentation limits the blast radius of a compromised device.
6. Address Supply Chain Vulnerabilities
IoT devices often rely on multiple vendors, software suppliers, OEMs, and integrators. Each stage introduces potential weaknesses.
Supply chain best practices:
- Request and review Software Bills of Materials (SBOMs)
- Priorities vendors with transparent security processes
- Evaluate third-party libraries for vulnerabilities
- Require compliance certifications
Supply chain risks are increasing as global IoT production becomes more decentralized.
To explore how different devices must be securely integrated, see Integrating Different Smart Home Systems: Tips and Best Practices on Tech News Tips.
7. Deploy AI-Powered Monitoring and Threat Detection
AI helps detect threats by analysing device behaviour and spotting anomalies faster than human teams can.
AI monitors:
- Abnormal traffic spikes
- Unusual device commands
- Communication outside expected patterns
- Potential worm or botnet propagation
- Firmware tampering
AI-based monitoring is particularly helpful for large-scale IoT environments with thousands of devices.
8. Develop an Incident Response Plan Built for IoT
Even with strong security, attacks can still happen. An IoT-specific incident response plan ensures rapid containment.
Your plan should include:
- Device isolation procedures
- Real-time alerts and escalation paths
- Backup communication systems
- Detailed forensic analysis steps
- Recovery workflows
A fast response reduces downtime and prevents attackers from spreading across networks.
9. Follow Global IoT Security Regulations
Compliance ensures legal protection and market approval. It also guides best practices.
Key global frameworks:
- NIST IoT Cybersecurity Framework
- ISO/IEC 27400:2022
- EU Cyber Resilience Act
- UK PSTI Act
- UAE National Cybersecurity Strategy
- Pakistan National Cybersecurity Policy
Meeting these requirements strengthens trust between businesses, regulators, and users.
10. Train Teams and Support Users
Human error remains one of the biggest vulnerabilities in any organisation.
Training should include:
- Recognizing suspicious behaviors
- Proper onboarding of IoT devices
- Secure password and key management
- Reporting procedures
- Safety protocols for physical access
Clear documentation and user-friendly onboarding reduce misconfiguration.
The Future of IoT Security
In the coming years, IoT security will evolve toward:
- AI-driven autonomous threat response
- Quantum-safe encryption algorithms
- Mandatory SBOMs across industries
- Unified international security standards
- Deeper integration between IoT and cloud security platforms
IoT ecosystems are becoming more interconnected and more intelligent. Security must evolve with them.
Security Must Be Built In, Not Added Later
Great IoT security is not a feature. It is a design philosophy.
It requires layered protection, lifecycle management, and continuous monitoring. Organizations that invest in robust IoT security today will gain a long-term advantage in trust, reliability, and scalability.
A secure IoT strategy is not just protection. It is the foundation for innovation in a connected world.
References
Statista, IoT Connected Devices Worldwide
https://www.statista.com/statistics/1183457/iot-connected-devices-worldwide/?srsltid=AfmBOorGej2mr4FLby4ImPosA6Xls1bC6VnOG8148VPeKT5qzzO7u_jy
NIST Cybersecurity for IoT Program
https://www.nist.gov/itl/applied-cybersecurity/nist-cybersecurity-iot-program
ISO/IEC 27400:2022 Guidelines
https://www.iso.org/standard/44373.html
ENISA IoT and Smart Infrastructure Security Resources
https://www.enisa.europa.eu/news/enisa-news/your-must-have-iot-security-checklist-enisas-online-tool-for-iot-and-smart-infrastructures-security